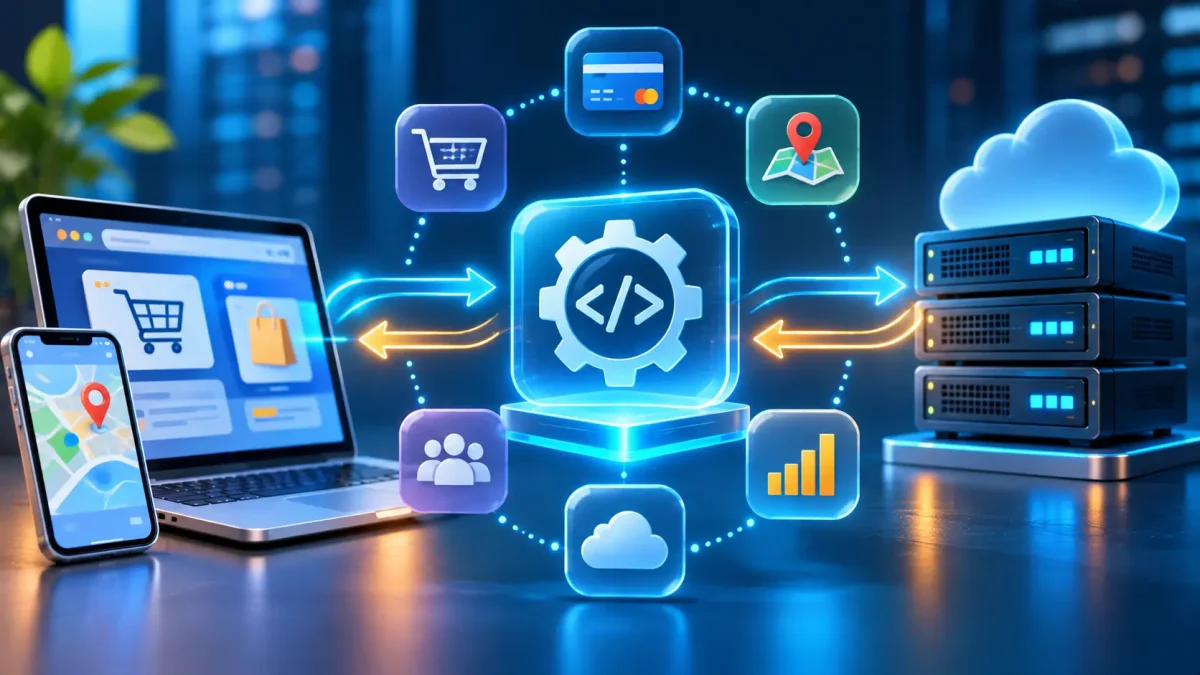
When you pay for an order on a website, view a map in an app, or sign in to a service with your Google account, different programs exchange data. They often use an API for this – a programming interface that defines how one system can communicate with another and receive the required response.
APIs are used on websites, in mobile apps, cloud platforms, and companies’ internal systems. In this article, we’ll explain what an API is, how requests and responses work, how the main types of interfaces differ, and how to safely try sending your first request.
What Is an API?
API is short for Application Programming Interface. In simple terms, it is a set of rules that allows one program to access the functions or data of another program. The interface defines which requests can be sent, what format the data must use, and what response to expect.
Imagine a restaurant. A customer does not go into the kitchen and look for ingredients. They choose a dish from the menu and give their order to a waiter. The waiter passes it to the kitchen, then brings the prepared dish or explains that the order cannot be fulfilled. In this analogy, the customer is the client program, the menu and ordering rules are the API, the kitchen is the server, and the prepared dish or error message is the response.
This example shows that an API does not necessarily reveal how a system works internally. The client program does not need to know exactly how the server stores information or performs an operation. It only needs to understand which actions are available and what data to provide. The service owner controls which functions and information are available through the interface.
So, an API is an agreed way for programs to interact. The question “what is an API?” often comes up when someone wants to understand how a website gets exchange rates, how a CRM sends orders to an accounting system, or how a mobile app loads a user profile. In each case, the API gives the programs shared rules for exchanging data.
The term API can also refer to operating system interfaces, a software library, or a web service. This article focuses mainly on web APIs – interfaces that programs use to communicate over a network. You can find a general explanation of APIs and examples in MDN’s learning material about web APIs.
How Does an API Work?
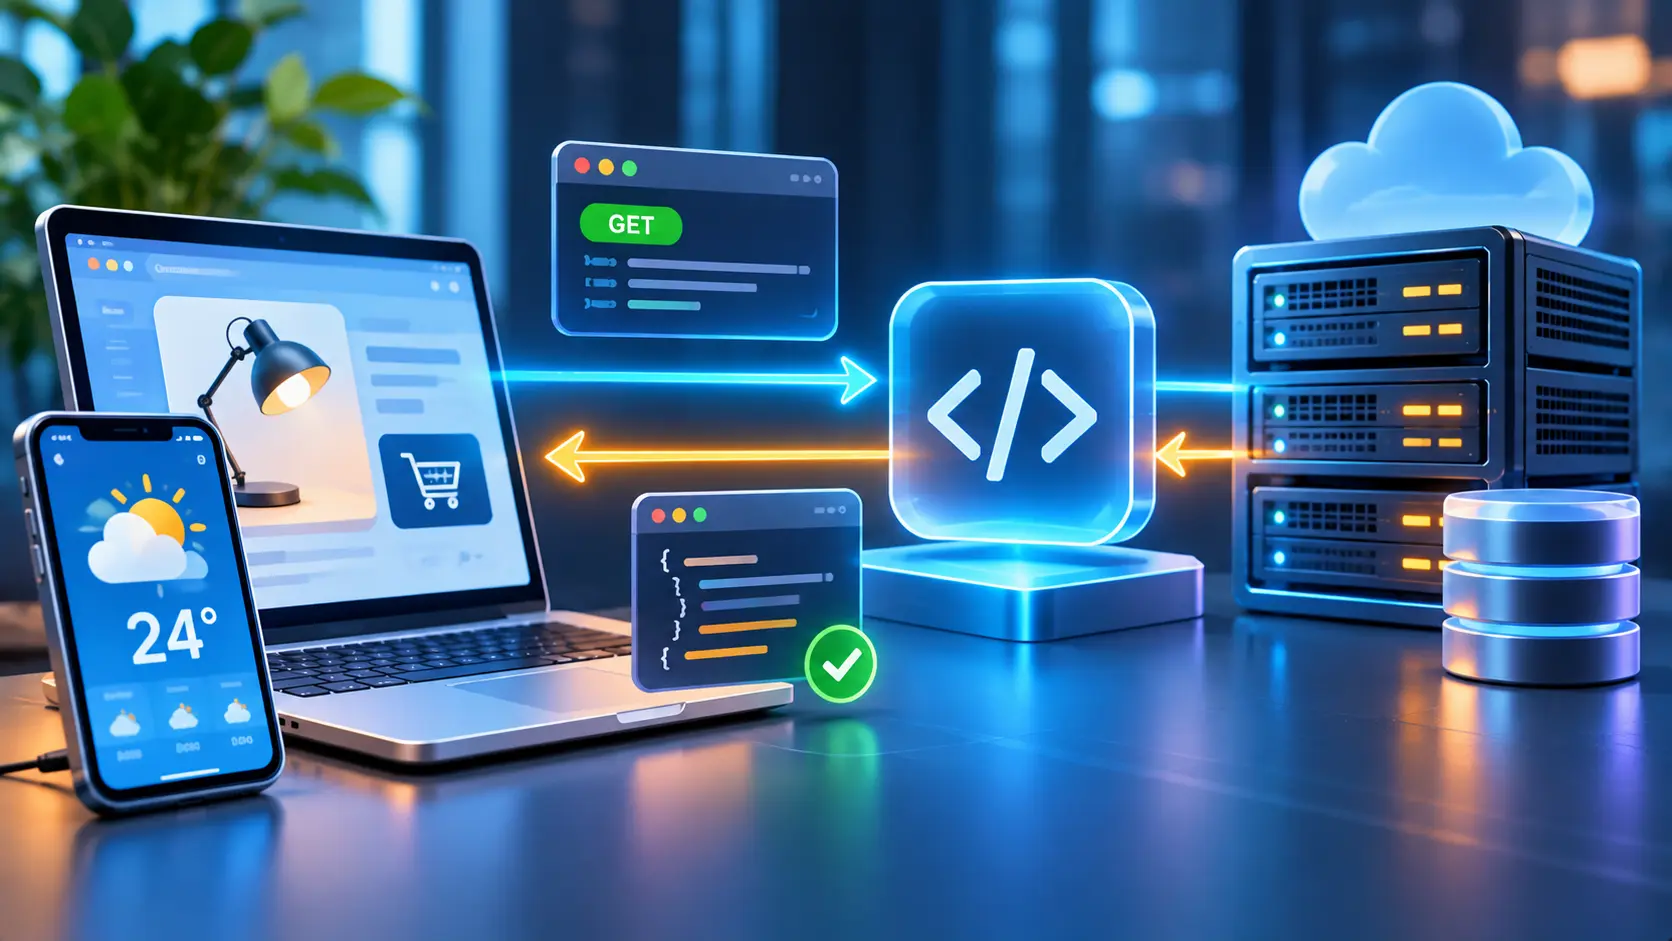
In a typical interaction, one program sends a request to another over a network. The server receives it, checks whether it is understandable and whether the client is allowed to perform the requested action, and then processes it. The result is a response: the requested data, a message confirming that the operation succeeded, or an error description.
For example, an online store may ask a delivery service for a list of branches in a selected city. The website sends the city and possibly other parameters. The service checks the request and returns a list of available addresses. The website shows this list to the customer. The API defines the format and rules for exchanging data, while the two services may have been created by different companies and use different technologies.
Many web APIs work over HTTP or HTTPS. In this case, a request contains a resource address, an HTTP method, headers, and, when needed, a body with data. A response usually has a status code, headers, and a body. Data is often sent in JSON format, but an API can use other formats, such as XML. The main principles of exchanging HTTP requests are described in MDN’s material about HTTP.
The Client–Server Interaction Principle
A client is a program or component that initiates a request. It may be a browser, a mobile app, an online store’s server, or an automated script. A server is a system that receives a request, processes it according to the API rules, and returns a result. In a particular scenario, one service’s server can also act as another service’s client.
For example, a user taps the “Show weather” button in a mobile app. The app sends a request to a weather service with coordinates or a city name. The service checks the parameters, retrieves the data for that request, and returns a response. The app reads it and displays the temperature, precipitation, or forecast. The user sees the result while the technical exchange happens in the background.
The steps may differ depending on the API, but the process generally looks like this:
- The client creates a request: it selects a resource address and method, then provides the required parameters.
- The request is sent over the network to the API server.
- The server checks the request format and whether the client can access the requested operation.
- The server performs the action or retrieves data from another system.
- The server sends a response, and the client checks its status and uses the result.
Not every request succeeds. The client may send an incorrect parameter, use an invalid token, or contact a service that is temporarily unavailable. A program should therefore account for possible errors as well as the expected result: it can show a clear message, offer to try again later, or avoid sending an unnecessary repeat request.
What Does an API Request and Server Response Look Like?
Let’s consider a hypothetical product catalog API that returns information about product number 42. A request might look like this:
GET https://api.example.com/products/42
Accept: application/json
Here, GET is the method indicating that the client wants to retrieve a resource; https://api.example.com is the service address; /products/42 is the path to the product with identifier 42; and the Accept header indicates that the client expects a response in JSON format. The example.com address is included only as an example; it is not a real service for testing the request.
A successful response may contain a status code and a JSON object:
HTTP/1.1 200 OK
Content-Type: application/json

{
 "id": 42,
 "name": "Table lamp",
 "price": 850,
 "available": true
}
The 200 OK code indicates that the request was processed successfully. The Content-Type header specifies the response body format. The JSON contains the product name, price, and availability status. The client can read these values and display a product card to the customer.
This is only an educational example. Real APIs may require an authorization token, additional parameters, or specific headers; the service documentation defines the field names and response format. A response may also contain an error instead of data – for example, 404 Not Found if the resource cannot be found, or 401 Unauthorized if the client has not been authenticated.
What Roles Do the GET, POST, PUT, and DELETE HTTP Methods Play?
An HTTP method describes the action the client is asking the server to perform on a resource. An API may implement these methods differently, so always check the documentation for the specific service. In general, these methods are used:
| Method | Typical purpose | Example |
| GET | Retrieve a resource or a list of data | Load data about a product or order |
| POST | Submit data for processing; often used to create a resource | Submit an order form or create a profile |
| PUT | Replace a resource with the supplied representation or create it, if the API allows this | Update all profile data |
| DELETE | Ask the server to delete a resource | Delete a saved address from a profile |
The difference between POST and PUT is not simply a matter of “create” versus “update.” Under HTTP semantics, PUT sends a representation of a resource to a known address and is idempotent: repeating the same request should produce the same desired state for the resource. POST submits data for processing according to the rules of a specific resource; a repeat may create another order or cause another side effect if the service does not prevent duplicates. The HTTP Semantics standard, RFC 9110, explains the purpose of these methods in more detail.
APIs often offer the PATCH method for partial updates. It is not included in this article’s list of four main methods, but it is important in practice: for example, it can be used to change only the phone number in a profile without sending the remaining fields.
Where Are APIs Used?
APIs are used whenever programs need to exchange data or delegate a function to one another. Users may not see this process: the interface hides the technical details and displays the result as a map, a payment button, a message, or a product list. Businesses can also use APIs to connect internal systems, automate data transfers, and reduce the need to enter the same information manually.
APIs for Websites and Online Stores
An online store can use APIs to communicate with a payment provider, delivery service, CRM system, email service, or accounting platform. After an order is placed, the website sends the payment system the amount and payment identifier. The payment service processes the transaction and returns its status, and the website displays the result to the customer. Payment data and the rules for processing it depend on the integration and the provider’s requirements.
Delivery is another common integration. A website sends the delivery service the address, parcel details, and order data, then receives a tracking number or a list of available branches. When the parcel status changes, the service can send an update to the store. The customer sees this information in their account or receives a notification.
A CRM integration can automatically send customer and purchase data to a customer relationship management system. The manager receives the information in their work tool, and employees do not need to enter the same data again. At the same time, the company must determine what data may be transferred, who can access it, and how integration failures are handled.
APIs in Mobile Apps
A phone app often uses APIs to sign in to an account and load a profile, order history, news, or messages. When a user changes a setting, the app can send the updated value to the server. The server saves the change and returns confirmation or explains why the operation could not be completed.
An app can also use APIs to retrieve data from a mapping service, display available payment methods, or synchronize information between devices. Permission to receive notifications or access geolocation is not, by itself, an API for a third-party service: it may also involve interaction with the phone operating system’s API.
Developers need to account for unstable connections, delays, and errors. For example, an app can save a form locally and offer to resend it when the connection is restored. However, automatically retrying a payment or order creation request without checking the result is risky: the server may have completed the operation even if the response did not reach the phone.
APIs for Integrating Third-Party Services
APIs make it possible to connect products that were developed separately. An analytics service may receive events from a website, a CRM may receive data from an advertising platform, and a corporate portal may display information from a human resources system. An integration can be one-way or two-way, depending on which requests and events the systems support.
For example, a company can synchronize a customer’s contact details between a CRM and an email marketing platform. When a user updates their email address, the change is sent to the other system. But automation does not mean that data is always synchronized instantly or without errors: access rules, limits, service availability, and conflict-handling logic all affect the process.
Some platforms support webhooks – a mechanism through which a service sends a message to a specified address after a particular event. For example, a payment system can notify a store that a payment status has changed. A webhook is not a complete replacement for an API: often, one service reports an event through a webhook, and another sends a separate API request to retrieve the details.
What Types of APIs Are There?
APIs are classified in different ways. By access, they may be interfaces available to a broad range of developers, internal interfaces used within an organization, or partner APIs. By interaction style or protocol, they may use REST, SOAP, GraphQL, RPC, or other approaches. These categories are not always mutually exclusive: an API can be restricted to partners while using REST as its interaction style.
Public, Private, and Partner APIs
A public API is intended for use by external developers. It may be open to everyone or require registration, an access key, acceptance of terms, or payment. “Public” does not mean that anyone has unrestricted access to all data: the API owner can set quotas, define which operations are allowed, and require authorization.
A private API is used within a company – for example, to connect a website to an internal warehouse or accounting system. Access is usually restricted by network, credentials, or corporate infrastructure rules. Its internal status does not remove the need for protection: a configuration error or compromised access can put data at risk.
A partner API gives access to specific companies or partners. It may require a contract, a separate onboarding process, a limited set of functions, or dedicated support. This format is used when organizations need to exchange data without opening the interface to everyone.
REST API, SOAP, GraphQL, and RPC
REST, SOAP, GraphQL, and RPC describe different approaches to organizing interactions. REST is an architectural style often used with HTTP: resources have addresses, and requests operate on them using standard methods. REST is not a separate network protocol. This approach is often chosen for web services with resources such as users, products, or orders.
SOAP is a message exchange protocol with a structure based on XML. It defines message formats and processing rules, and it can work with different transport protocols. SOAP is found in corporate systems where formal contracts and compatibility with existing infrastructure are important. The SOAP 1.2 description is published in the W3C specification.
GraphQL is a query language for APIs and a runtime for executing those queries on a server. The client specifies which fields and related data it needs, and the server returns a result that conforms to a defined schema. This can be useful when different screens need different sets of data. At the same time, the server needs to control query complexity and access to fields. The basics are described in the official GraphQL learning section.
RPC is an approach in which a client requests a remote operation as if it were calling a function or procedure. The name comes from Remote Procedure Call. RPC approaches can use different protocols and formats, including gRPC in services where consistent contracts and efficient communication between components are important.
There is no universally best approach. The choice depends on the task, speed and security requirements, the format of existing systems, the team’s expertise, and the needs of client applications. For an integration, it is important not only to compare technologies but also to check the documentation, API stability, support policy, and access terms.
What Are the Advantages and Disadvantages of Using an API?
An API gives systems a predictable way to interact, but the mere presence of an interface does not guarantee a reliable integration. Documentation quality, access control, error handling, and version support all matter. Before connecting a third-party service, it is important to understand both its capabilities and its limitations.
The main advantages of APIs:
- Automation. Data can be transferred between systems without manual copying, and routine operations can be performed according to defined rules.
- Function reuse. A service can provide payments, address lookup, or analytics without requiring every company to build that function itself.
- Development flexibility. The client side of a website, the server, and external services can change independently as long as compatible data exchange rules remain in place.
- Scalable integrations. With proper design, new channels or systems can be connected through a defined interface instead of rebuilding the entire product.
At the same time, APIs create dependencies and require technical maintenance. If a third-party service is unavailable, an integrated function may experience disruptions. Request limits restrict the rate of calls; version changes may require code updates; and different systems may interpret fields and errors differently. An integration also expands the attack surface, so authentication, authorization, and data control rules must be applied.
To reduce these risks, a team should monitor the availability of dependent services, check their change notices, keep an operation log, and plan for timeouts and repeated requests. For important business processes, it is useful to decide what users will see during an outage and how the system will resume an operation without creating duplicates.
How Do You Get Started with APIs?
Getting started depends on whether you want to integrate a service into your own product or simply understand how an API responds to requests. In the first case, you need to study the provider’s documentation and access rules. To learn, you can choose an API with public examples and send a test request using a dedicated tool without connecting it to live data.
Before integration, define the specific task: what data needs to be received or sent, when it should happen, and which system will use it. Then check whether an API exists for the function, what access terms apply, and whether the interface meets your product’s requirements. Test the integration outside the production environment, especially when requests can create orders, change user data, or charge money.
Where Can You Get an API Key and Documentation?
Look for documentation on the service’s official website under sections such as Developers, API, Documentation, or Integrations. It should describe request addresses, available methods, parameters, response format, authorization, limits, and examples. Before you start, also check whether a test environment is available, what data usage rules apply, and how to migrate to a new API version.
An API key is a string of characters that a service can use to identify an application or limit its access. However, an API key does not always verify a user’s identity and does not replace other authentication mechanisms. Some services use a key for quota management; others use it as part of an access scheme. Requirements vary, so check the documentation for the specific provider. Google also explains the difference between an API key and user credentials.
A key is usually created in a developer account after registering an application or project. The service may let you restrict its access to certain APIs, domains, or IP addresses. Do not publish secret keys in a public repository, on a web page, or in a public message. If a key is accidentally exposed, revoke it and create a new one. For a production project, store secrets in an appropriate vault rather than in code that is available to the browser.
How Do You Send an API Request and Check the Response?
For a first introduction to APIs, you can use Postman, a tool that lets you configure and send requests through a graphical interface. First, choose a request from the documentation, specify its method and address, and add the required headers and parameters. If the service requires a token or API key, use test credentials and pass them only in the way recommended by the provider.
After sending the request, check the status code, headers, and response body. Codes in the 2xx range usually indicate success; 4xx codes indicate a problem with the request or access; and 5xx codes indicate an error on the server side. The code alone is not enough to diagnose the issue: read the response body and the service documentation. Postman displays the response along with its status code, headers, and body, as described in the Postman documentation.
If you receive an error, check the address, method, required parameters, data format, and access permissions. Then compare the values with the example in the documentation. Do not repeatedly retry requests that create or modify resources without checking the result: a retry may duplicate the operation. If the server returns 429 Too Many Requests, the service has limited the request rate; the causes and troubleshooting options are described in Hostpark’s article about the 429 Too Many Requests error.
How Secure Is API Use?
The level of security depends on how the API and client integration are designed. Risks include stolen credentials, access to other people’s records due to insufficient permission checks, personal data leaks, incorrect configuration, and excessive resource consumption. The OWASP report on API security risks specifically covers authentication problems, access control, and unrestricted resource consumption.
Basic security measures should be appropriate for the specific API and the sensitivity of the data:
- Use HTTPS. HTTPS protects data in transit between the client and server using TLS, but it does not guarantee the security of the system itself or replace access control.
- Grant only the minimum required permissions. Limit access to functions and data according to the needs of the application or user.
- Store secrets properly. Do not embed private keys in public code or pass them in a URL, where they may end up in logs or browser history.
- Apply limits and monitoring. Quotas help control load, while logging helps detect unusual requests and errors.
- Rotate or revoke keys when necessary. If a secret is lost or may have been copied by someone else, revoke it and configure access again.
HTTPS protects the transmission channel but does not fix authorization errors: the server must still check whether a specific client can view or modify the requested resource. Similarly, an API key available in a browser should not be considered secret just because it looks complex. API security depends on server-side access restrictions and proper handling of credentials. Recommendations about keys and threats are provided in the OWASP REST Security Cheat Sheet and OWASP API Security Top 10.
Conclusion
An API is a set of rules that programs use to send requests to one another and receive responses. With an API, a website can interact with a payment system, an app can load data from a server, and business platforms can exchange information. Requests contain an address, a method, and the required data; a response can report success, return a result, or explain an error.
APIs simplify integration and automation, but they require careful attention to compatibility, access, and security. Before connecting a service, read its documentation, check the terms of use and limitations, test requests, and plan how to handle failures. This makes an API a predictable part of a product’s architecture rather than an unexpected dependency.
FAQ
Can You Use an API Without Knowing How to Code?
Yes. You can use Postman or another request testing tool to explore an API. Ongoing integration of an API into a website or app usually requires programming or a ready-made module that supports the service.
Are APIs Free?
The provider sets the terms. An API may be free, have a limited free quota, require a subscription, or charge based on the number of requests or resources used. Check the pricing and billing rules before connecting.
Does Every API Require an API Key?
No. Some interfaces are available without a key, while others use keys, tokens, OAuth, or multiple levels of authorization. The access method depends on the service and the data or operations it provides.
What Should You Do If an API Stops Responding?
Check the status code, network connection, documentation, and the service status page, if the provider has one. Make sure the key has not been revoked, the request is within the limit, and the API format and version are still current. Do not automatically retry operations that could create duplicates or charge money.
Are an API and an Integration the Same Thing?
No. An API is an interface and a set of access rules, while an integration is a connection implemented between systems. For an integration to work, a program must send requests according to the API documentation, process responses, and account for errors and limitations.